The rapid expansion of artificial intelligence infrastructure has introduced a new class of security risks that modern enterprises must navigate with extreme precision to protect their internal cloud environments. As organizations increasingly adopt the Model Context Protocol to streamline how AI
Decoupling AI from rigid infrastructure and single-vendor ecosystems is essential for building a mature and secure enterprise-grade technology stack. As of 2026, the transition from experimental generative tools to fully operational agentic workflows has become the primary objective for major
BlockAuditChain replaces vulnerable logs with a permissioned blockchain ledger that chains cryptographic hashes of every access request and policy decision. This specific innovation anchors the broader PrivGuardAI framework, which was developed to address escalating vulnerabilities within
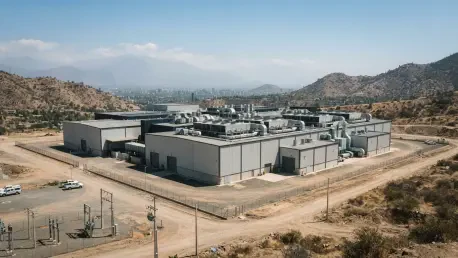
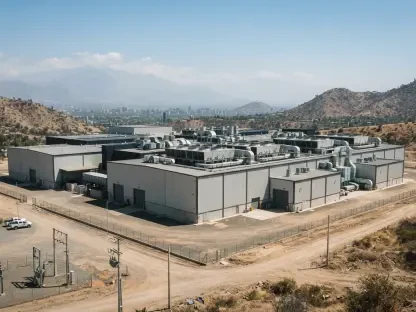
The arrival of a local AWS region provides a powerful competitive edge for Chilean startups looking to scale their artificial intelligence applications. This technological milestone represents a turning point for the Santiago Metropolitan Region, effectively positioning the nation as a premier
The sudden paralysis of critical digital infrastructure across Eastern Europe serves as a stark reminder that even the most robust cloud ecosystems are vulnerable to sophisticated cyber incursions. When ActiveCloud, a premier provider in Belarus, found its systems encrypted by ransomware, the
Phishing emails leveraged the specific 24-hour window following the outage to pressure staff into providing credentials under the threat of permanent message deletion. This calculated strategy capitalized on the inherent anxiety and disruption caused by the temporary failure of Exchange Online
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98 99 100 101 102 103 104 105 106 107 108 109 110 111 112 113 114 115 116 117 118 119 120 121 122 123 124 125 126 127 128 129 130 131 132 133 134 135 136 137 138 139 140 141 142 143 144 145 146 147 148 149 150 151 152 153 154 155 156 157 158 159 160 161 162 163 164 165 166 167 168 169 170 171 172 173 174 175 176 177 178 179 180