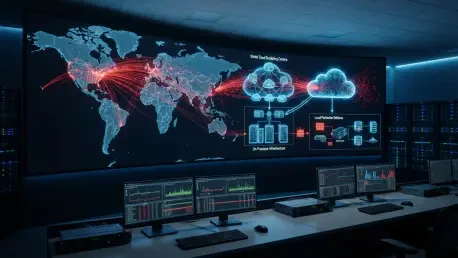
The shift toward behavioral analysis enables security teams to mitigate threats within encrypted traffic streams without sacrificing data privacy or performance. As the digital landscape matures in 2026, the reliance on purely cloud-based scrubbing services has given way to a more sophisticated architectural philosophy. While the previous decade was defined by a massive migration toward external mitigation providers, current infrastructure requirements demand a localized presence at the network edge. Organizations, especially those in the banking and telecommunications sectors, have recognized that the latency overhead and lack of visibility inherent in “redirect-and-clean” models can no longer support real-time application demands. Consequently, the integration of on-premises hardware with cloud-based burst capacity has become the gold standard for maintaining service availability in an environment where attack vectors are increasingly complex and localized.
The reintegration of on-premises mitigation is a strategic move to regain control over the network perimeter. For critical infrastructure providers, the decision to manage traffic locally is driven by the need for immediate responsiveness. A hybrid strategy allows for a nuanced approach where simple, high-volume volumetric attacks are signaled to the cloud for heavy-duty scrubbing, while more targeted, protocol-specific threats are handled at the source. This ensures that legitimate users experience minimal disruption, as the network logic remains close to the actual data flow. By blending the immediate defensive posture of on-site appliances with the massive scale of distributed cloud networks, enterprises achieve a level of resilience that was previously unattainable with a single-source solution.
Physical Boundaries: The Conflict Between Bandwidth and Local Logic
The fundamental limitation of any on-premises defense system remains the physical capacity of the incoming network pipes. When an organization faces a massive volumetric flood that exceeds its total internet link capacity, no amount of local processing power can prevent the link from saturating. This physical reality creates a “hard boundary” where local appliances become ineffective because the traffic cannot even reach them. In 2026, with the proliferation of high-speed fiber and massive botnet arrays, the discrepancy between attack volume and local link capacity has only widened. Therefore, the strategic placement of cloud-based “overflow valves” is essential to buffer the network. These external shields absorb the initial shock of a multi-terabit attack, ensuring that the local infrastructure remains reachable for legitimate traffic and local mitigation engines.
Navigating this boundary requires a coordinated signaling mechanism between local hardware and cloud providers. Modern infrastructure teams rely on automated triggers that detect link saturation thresholds and initiate traffic redirection before a total outage occurs. This allows the local security stack to focus on high-precision filtering rather than raw volume absorption. By treating the cloud as a secondary, elastic tier of the network, organizations can maintain a cost-effective local footprint while retaining access to the heavy-lifting capabilities of a global scrubbing network. This logistical calculation ensures that defense resources are allocated efficiently, preventing expensive local hardware from being overwhelmed by brute-force attacks that are better handled by the distributed nature of the cloud.
Computational Economics: The Role of Early Packet Filtering
The relationship between the point of filtration and the computational cost of processing malicious packets is a critical factor in modern network health. Every packet that bypasses initial edge filters consumes valuable CPU cycles and memory as it traverses routers, firewalls, and application load balancers. If malicious traffic is allowed to penetrate deep into the internal network stack, it can lead to resource exhaustion even if the target application is functionally robust. To prevent this, current defensive strategies emphasize filtering at the absolute ingress point. By identifying and discarding malicious packets at the very edge of the network, organizations preserve downstream compute resources for actual business logic and legitimate customer interactions, maintaining system performance during sustained assaults.
To facilitate this high-speed ingestion and evaluation, many security teams have turned to the Data Plane Development Kit (DPDK) and similar kernel-bypass technologies. These tools allow for the rapid processing of packets by bypassing the traditional overhead of standard operating system kernels, significantly increasing the throughput of local mitigation appliances. However, raw speed must be balanced with intelligent traffic classification to ensure that legitimate packets are not inadvertently dropped. The goal is to create a high-precision defensive layer that operates with the speed of a router but the intelligence of a security analyst. By stopping the majority of infrastructure-level threats at the edge, organizations can significantly reduce the overall operational burden on their internal servers and maintenance teams.
Ecosystem Defense: Mitigating the Noisy Neighbor Effect
Network and transport layer attacks, such as reflection and amplification floods, continue to pose a significant threat to infrastructure providers. These attacks exploit protocol weaknesses like DNS or NTP to overwhelm the target without requiring deep application-layer inspection. Because these threats focus on the underlying infrastructure rather than specific application logic, they are perfectly suited for mitigation at the local network perimeter. For hosting companies and Internet Service Providers managing thousands of disparate services, local filtering provides a broad protective umbrella. This centralized defense allows providers to shield their entire network footprint from protocol-level exploits without the need for complex, application-specific configurations for every individual client.
A primary benefit of this localized, infrastructure-wide defense is the prevention of the “noisy neighbor” effect. In a shared network environment, a massive attack directed at one customer can inadvertently consume the bandwidth and resources of everyone else on the same routing segment. By implementing robust local mitigation at the edge, providers can isolate and clean attack traffic before it enters the shared core of the network. This ensures that a single targeted assault does not degrade the service quality for unrelated clients. Local mitigation thus serves as a critical stabilization tool for the entire network ecosystem, allowing providers to offer higher service level agreements and maintain consistent performance even when portions of their infrastructure are under heavy bombardment.
Privacy and Visibility: Defending Encrypted Data Streams
The universal adoption of advanced encryption protocols, such as TLS 1.3 and QUIC, has redefined the requirements for traffic inspection. Traditionally, security tools relied on decrypting traffic to identify malicious signatures, but this approach has become increasingly impractical due to latency concerns and strict data privacy regulations. Furthermore, protocols like QUIC are encrypted by default, making traditional deep packet inspection a significant technical hurdle. In response, modern on-premises defense has pivoted toward behavioral analysis of connection metadata. Instead of looking at what is inside a packet, security systems now focus on how the connection behaves, using temporal patterns and protocol anomalies to identify malicious intent without compromising the integrity of the encrypted payload.
This move toward behavioral analysis allows organizations to maintain a high-speed defensive posture while respecting the privacy requirements of their users. By analyzing packet arrival rates, sequence numbers, and transport layer headers, security teams can detect botnet activity and sophisticated application-layer attacks with high accuracy. This metadata-driven approach avoids the performance penalties associated with decryption and re-encryption, which is vital for latency-sensitive applications like financial trading or real-time communication. As encryption becomes more deeply integrated into the fabric of the internet, the ability to mitigate threats without visibility into the underlying data has become a foundational requirement for any modern defense strategy, ensuring that security and privacy can coexist.
Structural Integration: The Multi-Layered Defense Approach
The most effective network resilience strategies in 2026 utilize a tiered, multi-layered architecture that mirrors the logic of modern data redundancy. This model treats the local mitigation layer and the cloud scrubbing layer as complementary components rather than competing solutions. The local layer is designed to handle day-to-day network threats and protocol-specific attacks, keeping sensitive traffic within the organization’s audited perimeter. This provides the lowest possible latency and maximum control over data sovereignty, which is a major concern for global enterprises operating in multiple jurisdictions. By handling the majority of threats locally, organizations reduce their reliance on third-party providers and maintain a more predictable operational environment.
The secondary cloud layer serves as an essential safety net for extreme scenarios. When a volumetric flood exceeds the physical thresholds of the local network, the architecture allows for a seamless “burst” into the cloud. This secondary tier also provides the computational scale necessary for deep inspection of complex application-layer threats that might be too resource-intensive for local appliances to handle. This hybrid structure offers a “best-of-both-worlds” scenario, where the organization maintains daily sovereignty and speed but retains the ability to scale its defense globally during a crisis. By segmenting defense based on the nature and scale of the attack, infrastructure teams have achieved a level of flexibility that ensures the network remains available regardless of the size or complexity of the incoming threat.
Strategic Implementation: The Path Toward Holistic Network Resilience
In previous cycles, the industry prioritized externalizing security to the cloud to simplify management and scale capacity quickly. However, the period from 2026 to 2028 marked a significant shift as organizations realized that total reliance on third-party providers created new vulnerabilities in terms of latency and data control. The resurgence of on-premises mitigation was not a return to legacy hardware silos, but a move toward software-defined security that integrated deeply with existing compute resources. Security leaders recognized that the most resilient posture involved placing defense logic as close to the data as possible, while maintaining a high-capacity escape route to the cloud. This dual-pronged approach successfully addressed the physical limitations of local bandwidth while providing the granular control needed for modern application security.
The move toward this hybrid model was further accelerated by the transition to off-the-shelf server hardware and software-defined networking. By decoupling security functions from proprietary appliances, enterprises gained the ability to scale their mitigation capabilities alongside their general purpose computing power. This transition proved that effective defense required a combination of high-speed local filtering and massive cloud-based buffering. Moving forward, the industry understood that maintaining service availability was not just about raw capacity, but about the intelligent orchestration of defensive resources across the entire network path. The ultimate success of these strategies rested on the ability of security teams to move fluidly between local and cloud environments, ensuring that the network remained a secure and performant foundation for the digital economy.