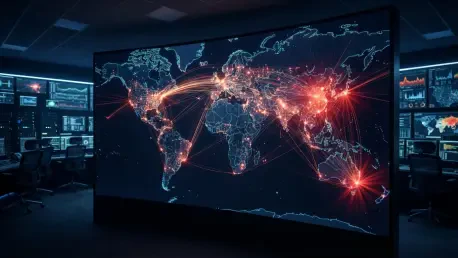
Connectionless Lightweight Directory Access Protocol abuse plummeted by nearly one hundred percent as attackers pivoted toward more effective DNS amplification methods. This radical shift signifies a deeper transformation in the global cyber-threat landscape as we navigate through the current year. While high-capacity mega-attacks exceeding 1 terabit per second dropped by nearly 70 percent, the total volume of network-layer disruptions skyrocketed to 18.2 million incidents in a single quarter. This 208 percent annual increase indicates that the decline of massive floods does not equate to a safer digital environment. Instead, the baseline of malicious activity has become more crowded than ever, with systems mitigating an average of 8,226 attacks every hour. Successful law enforcement operations disrupted four major botnets earlier this year, yet the sheer persistence of threat actors has shifted the defensive focus from occasional massive surges to a constant, high-volume pressure of digital harassment that impacts every sector.
Evolving Tactics and Industry Targets
Technical Shifts: The Rise of DNS and UDP Floods
The technical agility of modern threat actors is most evident in their rapid rotation of protocols to bypass traditional static defenses. While CLDAP abuse became nearly non-existent, Domain Name System (DNS) amplification attacks surged by 215 percent, representing a significant portion of network-layer activity. Simultaneously, generic User Datagram Protocol (UDP) floods rose from 14 percent to over 31 percent of all mitigated traffic. Despite these shifting preferences, plain DNS floods maintained their position as the primary weapon for disruption, accounting for nearly 40 percent of total attack volume. Even legacy threats have proven remarkably resilient; the infamous Mirai botnet, despite its age, generated a staggering 57.23 petabytes of traffic in a single month during the current year. One specific Mirai-driven event lasted nearly 50 hours, illustrating that while new methods emerge, older variants are being continuously refined to maintain a state of persistent operational chaos across the internet.
Global Realignments: Geographical and Industrial Targets
Geopolitical tensions and economic shifts have directly influenced the geographical distribution of DDoS targets throughout this year. The United States reclaimed its position as the most-attacked nation, followed closely by Indonesia and China, but the most dramatic escalations occurred in Canada and Israel. Canada rose to the sixth most-targeted position, with hostile activity concentrated in the retail and telecommunications sectors amid ongoing bilateral trade disputes. Similarly, Israel experienced a surge to tenth place, driven largely by cyber warfare coinciding with parliamentary elections and regional religious holidays. These shifts demonstrate that digital disruption has become a preferred tool for signaling political discontent or applying economic pressure without physical conflict. The precision of these geographical spikes suggests a level of coordination that transcends simple random targeting. As global entities monitor these trends, it becomes clear that cyber defense is now inextricably linked to the broader geopolitical climate.
The Mandate for Automated Defense
Speed and Scale: The Failure of Manual Mitigation
The current era of digital threats is defined by the dominance of micro-attacks that are intentionally designed to be short-lived and low-bandwidth. Approximately 96 percent of the 18.2 million attacks recorded this year lasted less than ten minutes, and 98 percent maintained a bandwidth of less than 1 gigabit per second. These metrics are the unmistakable hallmark of DDoS-for-hire services, commonly known as booter platforms. These services allow unskilled actors to launch surgical strikes for a nominal fee, often used for personal vendettas or minor disruptions that nonetheless paralyze unprotected websites. Because these incidents frequently conclude before a human analyst can even receive or acknowledge a system alert, manual intervention has become fundamentally obsolete. The speed of execution in these micro-attacks creates a defensive gap that can only be bridged by systems capable of millisecond-scale detection. Relying on traditional security operations centers to manually mitigate such rapid events is a failing strategy.
Future Resilience: Building Autonomous Security Systems
The emergence of new botnet variants like Dysphoria confirmed that the vacuum created by law enforcement actions was filled immediately by more sophisticated tools. This rapid evolution necessitated a fundamental shift toward AI-driven, automated mitigation systems that operated without the need for constant human oversight. Organizations that successfully maintained stability throughout this year moved away from reactive postures and embraced proactive, autonomous defenses. These systems utilized machine learning to identify anomalous traffic patterns in real-time, neutralizing threats before they could impact the end-user experience. It was recommended that businesses prioritize the integration of edge-based security layers that could scale dynamically with the volume of incoming traffic. This approach ensured that even the most persistent UDP and DNS floods were mitigated at the network perimeter. Ultimately, the industry recognized that manual oversight in a landscape of sub-ten-minute attacks was no longer a viable strategy for protecting digital infrastructure.