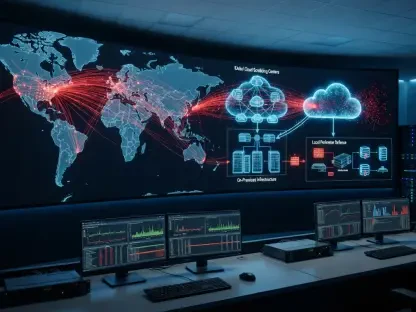
The vulnerability within the AWS Systems Manager Agent underscores the necessity for defense-in-depth strategies when managing remote commands across diverse server environments. As cloud architectures become increasingly complex, the tools designed to simplify their management often become the
A sudden and aggressive spike in automated mass-scanning activities has recently begun targeting exposed Vite development servers across various global network segments. This specific vulnerability, identified as CVE-2026-39364, carries a significant CVSS score of 7.5 and represents a dangerous
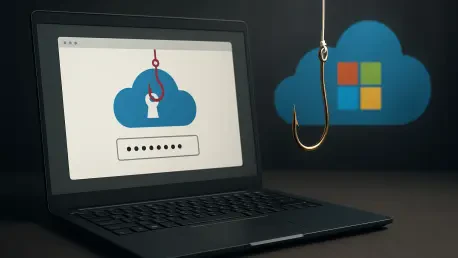
Once initial access is secured, attackers utilize the Microsoft Graph API to programmatically map organizational structures and identify the location of sensitive SharePoint and OneDrive repositories. This methodical execution underscores a significant trend in the 2026 threat landscape, where the
Static analysis often misses high-risk anomalies, such as a compromised backup service suddenly attempting to execute administrative configuration changes. In the current landscape of 2026, cloud environments have expanded far beyond simple human-operated accounts, now encompassing an intricate web
A critical vulnerability in a primary identity provider can instantly compromise authentication services for thousands of downstream corporate clients at once. This systemic risk was starkly demonstrated in the middle of 2026 when a zero-day exploit targeting Oracle PeopleSoft management layers
The implementation of compact public proofs allows third-party auditors to confirm data consistency mathematically without needing access to secret decryption keys. In the current 2026 technological landscape, where the sheer volume of global data necessitates complex storage solutions,